

Updated Nov 14, 2021 Test Engine to Practice Test for 312-50v11 Valid and Updated Dumps
Exam Questions for 312-50v11 Updated Versions With Test Engine
Audiences that Can Aim at 312-50v11
Think of investing time and efforts in this EC-Council 312-50v11 exam only if your operational areas are linked to penetration testing, vulnerabilities testing, and the like. Also, specialists like auditors, security officers, site administrators, and security employees will earn high profits from such an exam.
NEW QUESTION 294
John, a professional hacker, decided to use DNS to perform data exfiltration on a target network, in this process, he embedded malicious data into the DNS protocol packets that even DNSSEC cannot detect. Using this technique. John successfully injected malware to bypass a firewall and maintained communication with the victim machine and C&C server. What is the technique employed by John to bypass the firewall?
- A. DNS enumeration
- B. DNS tunneling method
- C. DNS cache snooping
- D. DNSSEC zone walking
Answer: B
Explanation:
DNS tunneling may be a method wont to send data over the DNS protocol, a protocol which has never been intended for data transfer. due to that, people tend to overlook it and it's become a well-liked but effective tool in many attacks. Most popular use case for DNS tunneling is obtaining free internet through bypassing captive portals at airports, hotels, or if you are feeling patient the not-so-cheap on the wing Wi-Fi. On those shared internet hotspots HTTP traffic is blocked until a username/password is provided, however DNS traffic is usually still allowed within the background: we will encode our HTTP traffic over DNS and voila, we've internet access. This sounds fun but reality is, browsing anything on DNS tunneling is slow. Like, back to 1998 slow. Another more dangerous use of DNS tunneling would be bypassing network security devices (Firewalls, DLP appliances...) to line up an immediate and unmonitored communications channel on an organisation's network. Possibilities here are endless: Data exfiltration, fixing another penetration testing tool... you name it. To make it even more worrying, there's an outsized amount of easy to use DNS tunneling tools out there. There's even a minimum of one VPN over DNS protocol provider (warning: the planning of the web site is hideous, making me doubt on the legitimacy of it). As a pentester all this is often great, as a network admin not such a lot .
How does it work:
For those that ignoramus about DNS protocol but still made it here, i feel you deserve a really brief explanation on what DNS does: DNS is sort of a phonebook for the web , it translates URLs (human-friendly language, the person's name), into an IP address (machine-friendly language, the phone number). That helps us remember many websites, same as we will remember many people's names. For those that know what DNS is i might suggest looking here for a fast refresh on DNS protocol, but briefly what you would like to understand is: * A Record: Maps a website name to an IP address. example.com ? 12.34.52.67 * NS Record (a.k.a. Nameserver record): Maps a website name to an inventory of DNS servers, just in case our website is hosted in multiple servers. example.com ? server1.example.com, server2.example.com Who is involved in DNS tunneling? * Client. Will launch DNS requests with data in them to a website . * One Domain that we will configure. So DNS servers will redirect its requests to an outlined server of our own. * Server. this is often the defined nameserver which can ultimately receive the DNS requests. The 6 Steps in DNS tunneling (simplified): 1. The client encodes data during a DNS request. The way it does this is often by prepending a bit of knowledge within the domain of the request. for instance : mypieceofdata.server1.example.com 2. The DNS request goes bent a DNS server. 3. The DNS server finds out the A register of your domain with the IP address of your server. 4. The request for mypieceofdata.server1.example.com is forwarded to the server. 5. The server processes regardless of the mypieceofdata was alleged to do. Let's assume it had been an HTTP request. 6. The server replies back over DNS and woop woop, we've got signal.
NEW QUESTION 295
You work for Acme Corporation as Sales Manager. The company has tight network security restrictions. You are trying to steal data from the company's Sales database (Sales.xls) and transfer them to your home computer. Your company filters and monitors traffic that leaves from the internal network to the Internet. How will you achieve this without raising suspicion?
- A. Encrypt the Sales.xls using PGP and e-mail it to your personal gmail account
- B. Change the extension of Sales.xls to sales.txt and upload them as attachment to your hotmail account
- C. Package the Sales.xls using Trojan wrappers and telnet them back your home computer
- D. You can conceal the Sales.xls database in another file like photo.jpg or other files and send it out in an innocent looking email or file transfer using Steganography techniques
Answer: D
NEW QUESTION 296
Dorian is sending a digitally signed email to Poly. With which key is Dorian signing this message and how is Poly validating it?
- A. Dorian is signing the message with his public key, and Poly will verify that the message came from Dorian by using Dorian's private key.
- B. Dorian is signing the message with Poly's private key, and Poly will verify that the message came from Dorian by using Dorian's public key.
- C. Dorian is signing the message with Poly's public key, and Poly will verify that the message came from Dorian by using Dorian's public key.
- D. Dorian is signing the message with his private key, and Poly will verify that the message came from Dorian by using Dorian's public key.
Answer: D
NEW QUESTION 297
Henry is a penetration tester who works for XYZ organization. While performing enumeration on a client organization, he queries the DNS server for a specific cached DNS record. Further, by using this cached record, he determines the sites recently visited by the organization's user. What is the enumeration technique used by Henry on the organization?
- A. DNS zone walking
- B. DNS cache poisoning
- C. DNS cache snooping
- D. DNS SEC zone walking
Answer: B
NEW QUESTION 298
John, a security analyst working for an organization, found a critical vulnerability on the organization's LAN that allows him to view financial and personal information about the rest of the employees. Before reporting the vulnerability, he examines the information shown by the vulnerability for two days without disclosing any information to third parties or other internal employees. He does so out of curiosity about the other employees and may take advantage of this information later. What would John be considered as?
- A. Acybercriminal
- B. Gray hat
- C. White hat
- D. Black hat
Answer: A
NEW QUESTION 299
A DDoS attack is performed at layer 7 to take down web infrastructure. Partial HTTP requests are sent to the web infrastructure or applications. Upon receiving a partial request, the target servers opens multiple connections and keeps waiting for the requests to complete.
Which attack is being described here?
- A. Session splicing
- B. Slowloris attack
- C. Phlashing
- D. Desynchronization
Answer: B
NEW QUESTION 300
jane invites her friends Alice and John over for a LAN party. Alice and John access Jane's wireless network without a password. However. Jane has a long, complex password on her router. What attack has likely occurred?
- A. Wardriving
- B. Piggybacking
- C. Wireless sniffing
- D. Evil twin
Answer: D
Explanation:
An evil twin may be a fraudulent Wi-Fi access point that appears to be legitimate but is about up to pay attention to wireless communications.[1] The evil twin is that the wireless LAN equivalent of the phishing scam. This type of attack could also be wont to steal the passwords of unsuspecting users, either by monitoring their connections or by phishing, which involves fixing a fraudulent internet site and luring people there. The attacker snoops on Internet traffic employing a bogus wireless access point. Unwitting web users could also be invited to log into the attacker's server, prompting them to enter sensitive information like usernames and passwords. Often, users are unaware they need been duped until well after the incident has occurred. When users log into unsecured (non-HTTPS) bank or e-mail accounts, the attacker intercepts the transaction, since it's sent through their equipment. The attacker is additionally ready to hook up with other networks related to the users' credentials. Fake access points are found out by configuring a wireless card to act as an access point (known as HostAP). they're hard to trace since they will be shut off instantly. The counterfeit access point could also be given an equivalent SSID and BSSID as a close-by Wi-Fi network. The evil twin are often configured to pass Internet traffic through to the legitimate access point while monitoring the victim's connection, or it can simply say the system is temporarily unavailable after obtaining a username and password.
NEW QUESTION 301
Which of the following LM hashes represent a password of less than 8 characters? (Choose two.)
- A. E52CAC67419A9A224A3B108F3FA6CB6D
- B. B757BF5C0D87772FAAD3B435B51404EE
- C. BA810DBA98995F1817306D272A9441BB
- D. CEC52EB9C8E3455DC2265B23734E0DAC
- E. 0182BD0BD4444BF836077A718CCDF409
- F. 44EFCE164AB921CQAAD3B435B51404EE
Answer: B,F
NEW QUESTION 302
There are multiple cloud deployment options depending on how isolated a customer's resources are from those of other customers. Shared environments share the costs and allow each customer to enjoy lower operations expenses. One solution is for a customer to join with a group of users or organizations to share a cloud environment.
What is this cloud deployment option called?
- A. Public
- B. Private
- C. Community
- D. Hybrid
Answer: C
NEW QUESTION 303
What is the common name for a vulnerability disclosure program opened by companies in platforms such as HackerOne?
- A. White-hat hacking program
- B. Bug bounty program
- C. Ethical hacking program
- D. Vulnerability hunting program
Answer: B
NEW QUESTION 304
Which of the following tools can be used for passive OS fingerprinting?
- A. nmap
- B. ping
- C. tracert
- D. tcpdump
Answer: D
NEW QUESTION 305
In the context of password security, a simple dictionary attack involves loading a dictionary file (a text file full of dictionary words) into a cracking application such as L0phtCrack or John the Ripper, and running it against user accounts located by the application. The larger the word and word fragment selection, the more effective the dictionary attack is. The brute force method is the most inclusive, although slow. It usually tries every possible letter and number combination in its automated exploration. If you would use both brute force and dictionary methods combined together to have variation of words, what would you call such an attack?
- A. BruteDics
- B. Hybrid
- C. Thorough
- D. Full Blown
Answer: B
NEW QUESTION 306
Richard, an attacker, aimed to hack loT devices connected to a target network. In this process. Richard recorded the frequency required to share information between connected devices. After obtaining the frequency, he captured the original data when commands were initiated by the connected devices. Once the original data were collected, he used free tools such as URH to segregate the command sequence. Subsequently, he started injecting the segregated command sequence on the same frequency into the loT network, which repeats the captured signals of the devices. What Is the type of attack performed by Richard In the above scenario?
- A. Reconnaissance attack
Cryptanalysis is that the science of cracking codes and secret writing secrets. it's accustomed violate authentication schemes, to interrupt scientific discipline protocols, and, additional benignantly, to seek out and proper weaknesses in coding algorithms.
It may be employed in IW applications - for instance, shaping Associate in Nursing encrypted signal to be accepted as authentic. Competitors UN agency are ready to discover the key can currently need to use it to their advantage, thus they're going to need to send phony encrypted messages to the supply so as to gain data or gain a bonus. It might even be used to pretend to be the supply so as to send phony data to others, UN agency currently can assume that it came from the official supply.
Among the kinds of attacks are:
Ciphertext solely attacks
best-known plaintext attacks
Chosen plaintext attacks
Chosen ciphertext attacks
Man-in-the-middle attacks
aspect channel attacks
Brute force attacks
Birthday attacks
There are variety of different technical and non-technical cryptography attacks to that systems will fall victim. cryptographical attacks may be mounted not solely against coding algorithms, however conjointly against digital signature algorithms, MACing algorithms and pseudo-random variety generators.
Ciphertext solely Attack
A ciphertext solely attack (COA) could be a case within which solely the encrypted message is accessible for attack, however as a result of the language is thought a frequency analysis may be tried. during this state of affairs the aggressor doesn't apprehend something concerning the contents of the message, and should work from ciphertext solely. - B. CrypTanalysis attack
- C. Side-channel attack
- D. Replay attack
Answer: B
NEW QUESTION 307
Leverox Solutions hired Arnold, a security professional, for the threat intelligence process. Arnold collected information about specific threats against the organization. From this information, he retrieved contextual information about security events and incidents that helped him disclose potential risks and gain insight into attacker methodologies. He collected the information from sources such as humans, social media, and chat rooms as well as from events that resulted in cyberattacks. In this process, he also prepared a report that includes identified malicious activities, recommended courses of action, and warnings for emerging attacks. What is the type of threat intelligence collected by Arnold in the above scenario?
- A. Tactical threat intelligence
- B. Operational threat intelligence
- C. Strategic threat intelligence
- D. Technical threat intelligence
Answer: C
NEW QUESTION 308
While browsing his Facebook teed, Matt sees a picture one of his friends posted with the caption. "Learn more about your friends!", as well as a number of personal questions. Matt is suspicious and texts his friend, who confirms that he did indeed post it. With assurance that the post is legitimate. Matt responds to the questions on the post, a few days later. Mates bank account has been accessed, and the password has been changed. What most likely happened?
- A. Matt's bank-account login information was brute forced.
- B. Matt inadvertently provided the answers to his security questions when responding to the post.
- C. Matt's computer was infected with a keylogger.
- D. Matt Inadvertently provided his password when responding to the post.
Answer: B
NEW QUESTION 309
Which of the following protocols can be used to secure an LDAP service against anonymous queries?
- A. SSO
- B. WPA
- C. RADIUS
- D. NTLM
Answer: C
NEW QUESTION 310
What is the following command used for?
sqlmap.py-u
,,http://10.10.1.20/?p=1
&forumaction=search" -dbs
- A. Retrieving SQL statements being executed on the database
- B. A Enumerating the databases in the DBMS for the URL
- C. Searching database statements at the IP address given
- D. Creating backdoors using SQL injection
Answer: D
NEW QUESTION 311
in an attempt to increase the security of your network, you Implement a solution that will help keep your wireless network undiscoverable and accessible only to those that know It. How do you accomplish this?
- A. Disable SSID broadcasting
- B. Lock all users
- C. Remove all passwords
- D. Delete the wireless network
Answer: A
NEW QUESTION 312
After an audit, the auditors Inform you that there is a critical finding that you must tackle Immediately. You read the audit report, and the problem is the service running on port 369. Which service Is this and how can you tackle the problem?
- A. The service is NTP. and you have to change It from UDP to TCP in order to encrypt it
- B. The findings do not require immediate actions and are only suggestions.
- C. The service is LDAP. and you must change it to 636. which is LDPAPS.
- D. The service is SMTP, and you must change it to SMIME. which is an encrypted way to send emails.
Answer: C
NEW QUESTION 313
Which of the following tools is used to detect wireless LANs using the 802.11a/b/g/n WLAN standards on a linux platform?
- A. Abel
- B. Kismet
- C. Nessus
- D. Netstumbler
Answer: B
NEW QUESTION 314
Morris, a professional hacker, performed a vulnerability scan on a target organization by sniffing the traffic on the network lo identify the active systems, network services, applications, and vulnerabilities. He also obtained the list of the users who are currently accessing the network. What is the type of vulnerability assessment that Morris performed on the target organization?
- A. Passive assessment
- B. internal assessment
- C. External assessment
- D. Credentialed assessment
Answer: D
Explanation:
Explanation
Detached weakness evaluation adopts an interesting strategy: In checking network traffic, it endeavors to order a hub's working framework, ports and benefits, and to find weaknesses a functioning scan like Nessus or Qualys probably won't discover on the grounds that ports are hindered or another host has come on the web.
The information may then give setting to security occasions, for example, relating with IDS alarms to lessen bogus positives.
Uninvolved investigation offers two key points of interest. The first is perceivability. There's regularly a wide hole between the thing you believe is running on your organization and what really is. Both organization and host scan report just what they see. Scan are obstructed by organization and host firewalls. In any event, when a host is live, the data accumulated is here and there restricted to flag checks and some noninvasive setup checks. In the event that your scan has the host certifications, it can question for more data, however bogus positives are an immense issue, you actually may not see everything. Further, rootkits that introduce themselves may run on a nonscanned port or, on account of UDP, may not react to an irregular test. On the off chance that a functioning weakness appraisal scan doesn't see it, it doesn't exist to the scan.
Host firewalls are regular even on worker PCs, so how would you identify a rebel worker or PC with a functioning output? An inactive sensor may see mavericks on the off chance that they're visiting on the organization; that is perceivability a scanner won't give you. A detached sensor likewise will recognize action to and from a port that isn't generally filtered, and may identify nonstandard port utilization, given the sensor can interpret and order the traffic. For instance, basic stream examination won't distinguish SSH or telnet on Port 80, however convention investigation may.
The subsequent significant favorable position of inactive investigation is that it's noninvasive- - it doesn't intrude on organization tasks. Dynamic weakness evaluation scanners are obtrusive and can disturb administrations, regardless of their designers' endeavors to limit the potential for blackouts. In any event, utilizing alleged safe sweeps, we've taken out switches, our NTP administration and a large group of other basic framework segments. Quite a long while prior, we even bobbed our center switch twice with a nmap port output.
NEW QUESTION 315
An attacker changes the profile information of a particular user (victim) on the target website. The attacker uses this string to update the victim's profile to a text file and then submit the data to the attacker's database.
<
iframe src=""http://www.vulnweb.com/updateif.php"" style=""display:none""
> < /iframe >
What is this type of attack (that can use either HTTP GET or HTTP POST) called?
- A. Cross-Site Scripting
- B. SQL Injection
- C. Browser Hacking
- D. Cross-Site Request Forgery
Answer: D
NEW QUESTION 316 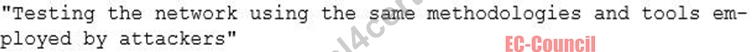
Identify the correct terminology that defines the above statement.
- A. Penetration Testing
- B. Designing Network Security
- C. Security Policy Implementation
- D. Vulnerability Scanning
Answer: A
NEW QUESTION 317
You are a penetration tester working to test the user awareness of the employees of the client xyz. You harvested two employees' emails from some public sources and are creating a client-side backdoor to send it to the employees via email. Which stage of the cyber kill chain are you at?
- A. Exploitation
- B. Reconnaissance
- C. Weaponization
- D. Command and control
Answer: A
Explanation:
At this stage exploiting a vulnerability to execute code on victim's direction channel for remote manipulation of victim is that the objective. Here ancient hardening measures add resiliency, however custom defense capabilities are necessary to prevent zero-day exploits at this stage. once the weapon is delivered to victim host, exploitation triggers intruders' code. Most often, exploitation targets Associate in Nursing application or software vulnerability, however it may additionally additional merely exploit the users themselves or leverage Associate in Nursing software feature that auto-executes code. In recent years this has become a district of experience within the hacking community that is commonly incontestible at events like Blackhat, Defcon and also the like.
NEW QUESTION 318
When discussing passwords, what is considered a brute force attack?
- A. You threaten to use the rubber hose on someone unless they reveal their password
- B. You create hashes of a large number of words and compare it with the encrypted passwords
- C. You wait until the password expires
- D. You attempt every single possibility until you exhaust all possible combinations or discover the password
- E. You load a dictionary of words into your cracking program
Answer: D
NEW QUESTION 319
......
312-50v11 Exam Dumps - Free Demo & 365 Day Updates: https://www.actual4cert.com/312-50v11-real-questions.html
Pass 312-50v11 Exam with Updated 312-50v11 Exam Dumps PDF: https://drive.google.com/open?id=1U4tCTvHtI0D7JURLOuSpm_QDWxum0kFJ